Welcome to the Bearded Viking Security Forge
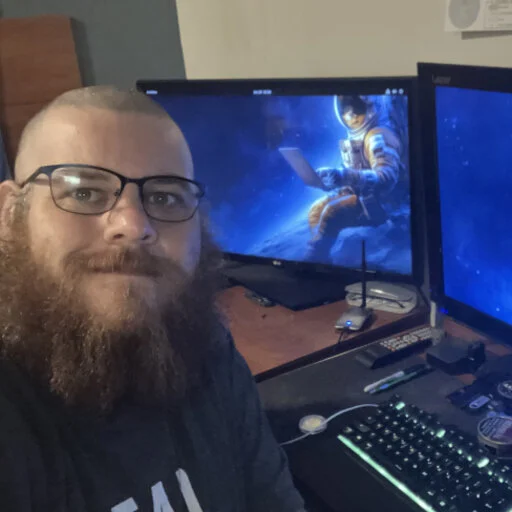
Welcome, fellow traveler of the digital frontier.
You have stumbled upon the Bearded Viking Security Forge — a sanctuary for those who seek knowledge, truth, and mastery in the art of cybersecurity. This is not just another security blog. This is a living document of one hacker's journey from the shadows of hacktivism to the forefront of ethical security research.
Who Is the Bearded Viking?
I am a former hacktivist who operated under the banners of Anonymous, LizardSquad, and LulzSec. I have seen the inside of government networks, corporate databases, and the darkest corners of the internet. I have exposed secrets, exploited vulnerabilities, and walked the thin line between chaos and justice.
But today, I am something different.
I am a Ph.D. in Computer Science, OSCP, CEH — and most importantly, a professional security researcher who helps organizations build unbreakable fortresses. I have found vulnerabilities in platforms like Google, Microsoft, Amazon, and CashApp. I have earned $250,000+ in bug bounties and helped secure the digital lives of millions.
And now, I am sharing everything I know.
What You'll Find Here
This blog is my digital war room — a place where I document my findings, share my insights, and teach the next generation of security professionals. Here's what you can expect:
- Bug Bounty Write-Ups: Detailed reports of vulnerabilities I've discovered, including exploitation techniques, impact analysis, and remediation guidance.
- Security Research: Deep dives into emerging threats, zero-day vulnerabilities, and cutting-edge attack vectors.
- Technical Tutorials: Step-by-step guides on tools, techniques, and methodologies for ethical hacking and penetration testing.
- Industry Commentary: My take on the latest cybersecurity news, breaches, and industry trends.
- Personal Reflections: The human side of security — the challenges, the victories, and the lessons learned along the way.
Where Else to Find Me
I believe in sharing knowledge freely. That's why I cross-publish my content on multiple platforms to reach as many people as possible:
- 📘 Medium: I publish long-form articles on Medium, reaching a broader audience of tech enthusiasts and security professionals.
- 🐦 X (Twitter): Follow me on X for real-time security updates, bug bounty announcements, and daily insights.
- 📚 Reddit: Join the conversation on Reddit where I engage with the community and answer questions.
- 💻 GitHub: Check out my open-source security tools and scripts on GitHub.
- 🔗 LinkedIn: Connect with me professionally on LinkedIn.
Follow me everywhere to stay ahead of the threats.
My Bug Bounty Journey
I've been hunting bugs for over a decade. Some of my most memorable findings include:
- SQL Injection exposing full customer databases with credit cards and PII.
- IDOR vulnerabilities allowing price manipulation and unauthorized access.
- X11 Server Exposure enabling screen capture and keystroke monitoring.
- Hardcoded API Keys in Android APKs leading to production access.
- GraphQL introspection exposing sensitive data operations.
- Firebase Manipulation enabling full account takeover.
Every vulnerability tells a story. And I will be telling those stories here — in full technical detail, complete with code snippets, exploitation steps, and remediation advice.
Why This Matters
The world is becoming more connected every day. And with that connection comes unprecedented risk. Cyber attacks are no longer a matter of "if" but "when." The companies we trust with our data, the governments that protect us, the systems that run our lives — they are all vulnerable.
But knowledge is power. And the more we understand the threats, the better we can defend against them.
That's why I'm doing this. Not for fame. Not for fortune. But because I believe in a more secure future — one where the good guys have the upper hand.
What's Coming Next
I have a backlog of vulnerabilities to write about, tools to build, and research to share. Here's a preview of upcoming content:
- Web Application Security Series — A deep dive into OWASP Top 10 vulnerabilities.
- Mobile App Pentesting — How to analyze and exploit Android and iOS apps.
- Cloud Security — Auditing AWS, Azure, and GCP configurations.
- Bug Bounty Methodology — My proven approach to finding vulnerabilities.
- Live Walkthroughs — Real-time exploitation demonstrations.
Subscribe to stay updated — I'll be publishing new content every week.
Let's Connect
I'm always open to collaboration, questions, and discussions. If you're a fellow security researcher, a company looking for a security assessment, or just someone curious about the world of hacking — reach out.
Together, we can build a more secure future.
Stay curious. Stay vigilant. Stay secure.
— The Bearded Viking
Forged in fire. Hardened by experience. Securing the future.